IT in Manufacturing


Cyber security trends for 2025: The five levels of maturity

March 2025 IT in Manufacturing

As cyber attacks reach unprecedented levels, chief information security officers (CISOs) are increasingly burdened with the responsibility of safeguarding organisations. Recent research indicates that the number of cyber attacks has surged dramatically, highlighting the urgent need for enhanced cybersecurity measures across various sectors. Despite the growing threat landscape, a survey found that only 13% of organisations globally are considered ‘cyber mature’ enough to effectively mitigate and recover from cyber incidents. These mature organisations can recover 41% faster from attacks compared to those at the lower end of the maturity scale. Key factors contributing to this speed include having advanced security tools that can provide early warnings about risks, clearly defined processes for incident response, and reliable backup systems for critical data.
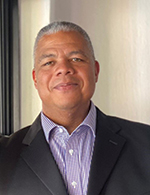

Graham Brown, country manager for SA/SADC at Commvault.

Determining CISO maturity levels

With the onus on CISOs to implement essential security measures, it is crucial for business leaders to evaluate whether they have the right individuals in place, supported by adequate resources. The authority of CISOs varies significantly across organisations, impacting overall cyber security maturity. At the initial stage, security responsibilities may fall to individuals who primarily follow orders, while at more advanced levels, CISOs engage with executive leadership to ensure cyber security is integrated into all aspects of business operations. To understand an organisation’s position within this maturity framework and its implications for cyber security risk and resilience, we can categorise the stages into the five following distinct levels:

Check box security: In organisations at this least mature level, security is often managed by IT staff who lack dedicated cyber security roles. Responsibilities are typically combined with routine IT tasks, such as server maintenance and software updates. These organisations may prioritise other business functions over security, leading to inadequate measures like multi-factor authentication being overlooked.

The right time for a CISO: As businesses grow, their exposure to cyber threats increases, prompting them to consider hiring a senior cyber security professional or CISO. At this stage, the role is often technical in nature, with limited opportunity for strategic planning. Compliance requirements begin to take precedence, necessitating formal monitoring and auditing processes.

Beyond a technical CISO: Organisations soon realise that CISOs require greater autonomy to implement security controls effectively. While decision making may still be limited to recommending technologies, CISOs must gain authority over broader measures that encompass cloud security and access management. This stage calls for strong collaboration between IT and security teams.

The empowered CISO: Approaching full maturity, CISOs participate in strategic discussions with senior management and advise on cyber security risks and recovery capabilities. They help define the organisation’s risk tolerance and develop strategies that align with business objectives while addressing emerging technologies like artificial intelligence.

Secure by design: At this ultimate level of maturity, security is embedded within the organisation’s culture and processes. Employees across all departments adhere to security protocols as part of their daily operations. Continuous testing of systems is standard practice, ensuring that teams are well prepared for incident response and data recovery.

Planning the maturity cycle

It is essential to recognise that no two organisations are alike when it comes to cyber security maturity. Each entity has its unique infrastructure, operational methods and strategic goals. Public companies will have different priorities compared to private ones, and larger organisations will face different challenges to smaller entities.

Measuring progress through the cyber security maturity cycle can be complex; however, understanding the characteristics of each stage allows business leaders to align their development efforts with their specific needs, whether through nurturing internal talent or recruiting skilled CISOs. This alignment will help build a level of maturity that matches their organisation’s risk tolerance as cyber threats continue to escalate into 2025 and beyond.


Share this article:
Share via emailShare via LinkedInPrint this page

Further reading:

Pilot project to optimise material flow
IT in Manufacturing
WEBER-HYDRAULIK has commissioned autonomous transport robots at its Güglingen site to handle internal material transport between warehouse and assembly areas. The pilot project uses RFID integration and SAP connectivity to automate material flows and reduce manual transport tasks.

Read more...
Accelerating pharmaceutical digital compliance and operational efficiency
Schneider Electric South Africa IT in Manufacturing
Cosmos Limited, one of Kenya’s leading pharmaceutical manufacturers, has partnered with Schneider Electric to implement an integrated monitoring, energy management and digital validation platform that has improved operational visibility, data integrity and regulatory compliance readiness.

Read more...
AI data centres, nature and innovation
Schneider Electric South Africa IT in Manufacturing
Artificial intelligence is driving unprecedented demand for data centre capacity, with liquid cooling now central to managing the heat generated by high-density GPU clusters. Schneider Electric examines how next-generation data centres can balance performance with environmental responsibility.

Read more...
Siemens powers next-generation reusable spacecraft development
Siemens South Africa IT in Manufacturing
A European aerospace startup focused on reusable space systems, has adopted Siemens Xcelerator software to connect engineering disciplines, reduce rework and accelerate spacecraft development, cutting the path from concept to flight hardware to nine months for its orbital demonstration capsule.

Read more...
How to navigate the high-stakes economics of AI infrastructure
IT in Manufacturing
Nearly 60% of data centre operators are expected to adopt liquid cooling within five years as AI workloads drive demand for higher rack densities. Understanding the full financial picture of liquid cooling, from capital investment to long-term operational savings, is now essential.

Read more...
Protecting the digital mine
RJ Connect IT in Manufacturing
As mining becomes increasingly connected and automated, cyber threats are emerging alongside the benefits of digitalisation. RJ Connect and provides rugged networking, edge computing and cybersecurity technologies from MOXA to help protect critical mining operations from evolving attacks.

Read more...
SICK launches AI-powered 3D quality inspection
SICK Automation Southern Africa IT in Manufacturing
SICK has combined deep learning with 3D height data analysis in its Nova machine vision platform.

Read more...
Predictive maintenance is the critical enabler for AI data centre liquid cooling systems
IT in Manufacturing
As liquid cooling becomes essential for AI data centres, predictive and condition-based maintenance are emerging as critical enablers of thermal stability. Schneider Electric argues that the infrastructure is already generating the data needed and the question is whether operators are equipped to use it.

Read more...
Siemens software scales with Simple Energy EV development
Siemens South Africa IT in Manufacturing
: Simple Energy, an Indian electric two-wheeler manufacturer, has expanded its use of Siemens Xcelerator software to manage complex vehicle variants and enterprise-level bills of materials, accelerating product development as its EV portfolio scales.

Read more...
ESG as a growth lever
RS South Africa IT in Manufacturing
Leading organisations are treating ESG not as a compliance obligation but as a practical tool for operational efficiency, supply chain resilience and business performance, with data and collaboration central to unlocking its value.

Read more...


While every effort has been made to ensure the accuracy of the information contained herein, the publisher and its agents cannot be held responsible for any errors contained, or any loss incurred as a result. Articles published do not necessarily reflect the views of the publishers. The editor reserves the right to alter or cut copy. Articles submitted are deemed to have been cleared for publication. Advertisements and company contact details are published as provided by the advertiser. Technews Publishing (Pty) Ltd cannot be held responsible for the accuracy or veracity of supplied material.


© Technews Publishing (Pty) Ltd | All Rights Reserved